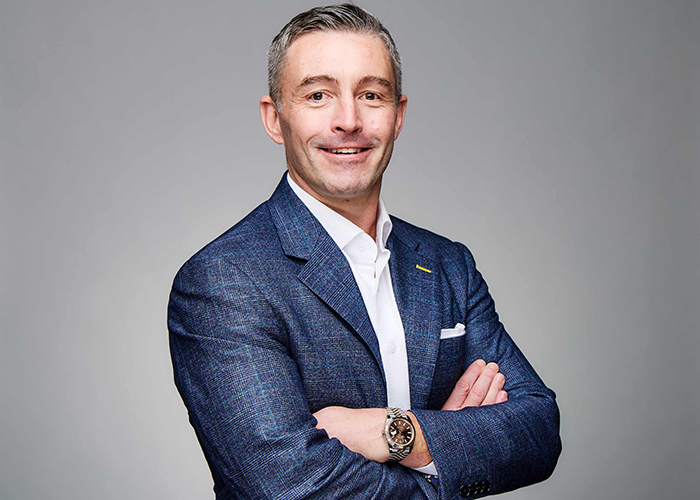
Singapore’s newly released Cybersecurity Strategy 2026 is prompting fresh questions for financial services organisations about how they govern identities, including non-human identities such as AI agents, according to commentary provided by Okta’s Asia Pacific and Japan leadership.
In remarks circulated by Okta, Dan Mountstephen, senior vice president and general manager for Asia Pacific and Japan, said the national strategy’s emphasis on continuous defence, AI deployment and closer coordination between government and industry heightens the need for organisations to understand “who, or what, is operating inside our systems”.
Mountstephen argued that banks, digital asset platforms and interbank networks are increasingly using autonomous AI agents to take privileged actions in real time, such as accessing data and triggering transactions. He said that as critical infrastructure protections expand, governance needs to extend to “the identities acting within that infrastructure, human or machine”.
The commentary also pointed to identity as an emerging attack path in what Mountstephen described as an “agentic environment”, citing examples such as forgotten service accounts, long-lived API keys and over-privileged agents.
Mountstephen linked these issues to the Monetary Authority of Singapore’s AI Risk Management Guidelines, saying they underscore that financial institutions remain accountable for the actions and outcomes of AI systems and third-party agents, and should expect to maintain inventories of AI use cases, lifecycle controls and continuous human oversight.
He outlined three identity-related controls he said are becoming foundational for scaling agentic automation in regulated environments: removing standing privilege by using short-lived, role-based tokens; treating agents as identities that are inventoried and bound to an audited human owner; and enforcing policy at runtime through gateways and “kill switches” to monitor and stop unauthorised actions.
The comments come as Singapore’s Cybersecurity Strategy 2026 sets out a national approach aimed at keeping defences current with evolving threats and strengthening resilience across the economy, including critical information infrastructure. For financial institutions, the debate is likely to centre on how identity and access management practices adapt as AI-driven automation becomes more embedded in operational workflows.