SIMBA Telecom, a Singapore-based mobile and broadband operator, disclosed on 25 September 2026 that it discovered a data breach the previous day affecting 23,549 registered customers.
According to the company, the exposed data includes names, NRIC numbers, dates of birth, mobile numbers and email addresses. SIMBA said no credit card or bank account information was at risk and that it had not seen indications the data had been misused at the time of its disclosure.
SIMBA said it has resolved the incident and is notifying affected customers by email. The company has not disclosed how the breach occurred.
SIMBA Telecom is owned by Tuas Limited, an Australian-listed company.
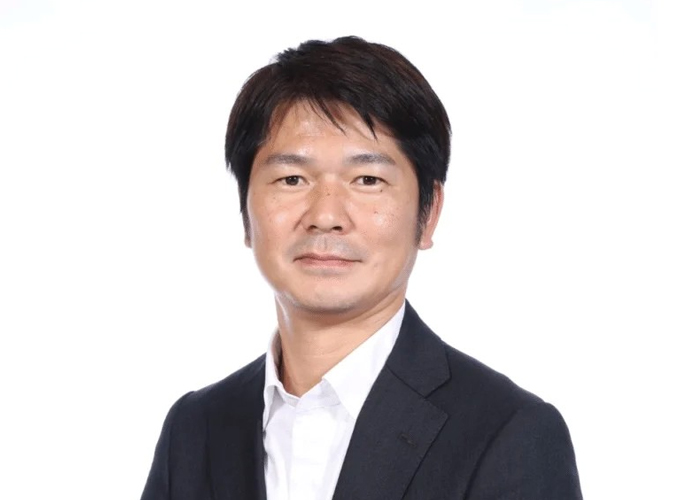
In comments provided by Keeper Security, Takanori Nishiyama, Senior Vice President APAC and Country Manager, Japan, said identity numbers and birth dates “cannot be reset like passwords once they are exposed” and could be exploited over long periods, particularly when paired with contact details that can make impersonation attempts more convincing.
Nishiyama pointed to guidance from Singapore’s Personal Data Protection Commission, which has asked private organisations to stop using identity numbers for authentication by the end of the year.
He argued that telecommunications subscriber registries are “high-value targets” because they contain verified identity data at scale, and said the SIMBA incident highlighted the risk posed by broad internal access rights where a single compromised account could expose an entire customer database.
Nishiyama cited the 2026 Verizon Data Breach Investigations Report, which found credential abuse was the initial access vector in 25% of Asia-Pacific breaches, second to vulnerability exploitation at 42%.
He said organisations should isolate subscriber data systems, restrict database access and adopt a “zero standing privilege” model for administrative access, including just-in-time access for approved tasks and auditing of sessions that access identity data.
“While subscribers cannot change their identity card numbers after a breach, organisations can still monitor, control and secure who has access to that important data,” Nishiyama said.